The 30-Day Microsoft 365 Governance Blueprint

Securing enterprise SharePoint Online repositories with Microsoft Purview data loss prevention policies and automated access reviews eliminates unauthorized sharing and maintains strict HIPAA and SOC 2 compliance. Applying granular Entra ID role-based access controls and encrypted document labels protects corporate intellectual property without impacting cross-functional workforce productivity.

Expert M365 and SharePoint architect consulting on The 30-Day Microsoft 365 Governance Blueprint. Zero-downtime migrations, secure compliance, custom solutions, and enterprise governance.

Implementation Guide

The 30-Day Microsoft 365 Governance Blueprint

You do not need six months to get governance under control. This is the exact 30-day plan I run with clients who need to be audit-defensible fast.

14-minute readIncludes templateBy Rohit Kumar

What Governance Actually Means in Microsoft 365

Governance is not a document. It is the combination of policy, technical control, automation, and evidence. If you can't demonstrate all four to an auditor, you don't have governance — you have a wish.

Week 1 — Baseline & Policy

  • Day 1–2: Executive kickoff, scope, RACI
  • Day 3–4: Inventory (Tenant, Groups, Teams, Sites, Apps, Flows)
  • Day 5: Draft the M365 Governance Policy (1-page)

Week 2 — Identity, Access & Data Classification

  • Enable Entra ID PIM for all admin roles; reduce global admins to ≤ 5
  • Deploy 4-tier sensitivity labels (Public / Internal / Confidential / Restricted)
  • Auto-labeling policies for known regex patterns (PII, PCI, financial data)
  • Conditional Access baseline: MFA, device compliance, risk-based sign-in

Week 3 — Lifecycle, DLP & External Sharing

  • Microsoft 365 Groups expiration policy (365 days, owner attestation)
  • Naming policy: {dept}-{purpose}-{sensitivity}
  • DLP policies for financial, HR, and IP content
  • External sharing model: default = new guests require approval; anonymous links disabled at tenant level

Week 4 — Evidence, Reporting, Handover

  • Automate weekly evidence pack via Power Automate + Microsoft Graph
  • Compliance Manager assessments aligned to your regulatory scope
  • Stand up a Governance Council: meets monthly, chaired by the CIO
  • Handover binder: policy, control matrix, runbooks, evidence samples

The Control Matrix (Template)

DomainControlToolEvidence
IdentityPrivileged access requires approvalEntra PIMPIM activation log
DataConfidential data is labeledPurviewLabel activity report
AccessQuarterly access reviewsEntra Access ReviewsReview completion report
SharingExternal guests are approvedEntitlement MgmtGuest lifecycle report

What Not To Do

  • Don't turn off external sharing tenant-wide — you'll break legitimate collaboration and drive shadow IT
  • Don't buy a governance tool before writing the policy — you'll automate chaos
  • Don't govern by exception — govern by design

Implementation Best Practices

When implementing this solution in your organization, consider these proven best practices that have delivered consistent results across enterprise deployments. Start with a pilot group of 5-10 users who represent different roles and technical comfort levels. This allows you to identify adoption challenges early and refine your approach before broader rollout.

Document every step of your implementation process. This documentation becomes invaluable for troubleshooting, training new team members, and demonstrating compliance during audits. Include screenshots, configuration screenshots, and decision rationales for each major choice.

Establish clear success metrics before you begin. These might include user adoption rates, time savings, error reduction, or compliance improvements. Measure baseline metrics before implementation and track progress at regular intervals (weekly for the first month, then monthly).

Common Pitfalls to Avoid

Based on experience across dozens of implementations, certain mistakes appear repeatedly. Avoiding these common pitfalls can save significant time and frustration. The most frequent error is insufficient stakeholder engagement—technical teams implement solutions without understanding business requirements, leading to low adoption.

Another common issue is underestimating the change management effort. Even technically superior solutions fail if users don't understand the value proposition or receive adequate training. Allocate 30-40% of your project timeline to communication, training, and support activities.

Don't neglect ongoing maintenance and governance. Many implementations fail not during initial deployment but in the months that follow when content becomes stale, permissions drift, and processes break down. Establish clear ownership and regular review cycles from day one.

Measuring Success and ROI

Quantifying the return on investment for Microsoft 365 initiatives requires a structured approach. Start by identifying the specific problems you're solving and their associated costs. These might include manual process hours, compliance risks, data loss incidents, or user productivity losses.

Establish baseline measurements before implementation. Track time spent on specific tasks, count error rates, survey user satisfaction, and document current process inefficiencies. These baselines provide the comparison point for post-implementation measurements.

After implementation, measure the same metrics at regular intervals. Calculate time savings, error reduction, productivity improvements, and risk mitigation. Translate these into financial terms where possible—hour savings times hourly rates, avoided compliance fines, reduced data recovery costs. Present these metrics to stakeholders to demonstrate value and secure support for ongoing initiatives.

Advanced Techniques and Optimizations

Once you have the foundation in place, consider these advanced techniques to maximize value from your Microsoft 365 investment. Automation through Power Platform can eliminate manual processes and reduce errors. Start with simple approval workflows and progress to more complex orchestrations as your team gains confidence.

Leverage Microsoft Graph API for custom integrations that connect M365 with other business systems. This enables scenarios like automated user provisioning, data synchronization, and cross-platform reporting. Work with experienced developers or partners for complex integrations.

Explore AI capabilities like Microsoft Copilot for productivity gains, but ensure proper governance and data classification first. AI tools amplify existing data quality and permission issues—address these foundations before AI deployment to avoid exposing sensitive information or generating inaccurate results.

Need help delivering this in your organization?

18+ years architecting Microsoft 365, SharePoint, and Power Platform for global enterprises.

Book a Strategy Call

Official Documentation & External Reference Resources

For further official technical specifications, security baselines, and video deep-dives, consult these verified Microsoft and professional resources:

Need Expert SharePoint, M365 & Power Platform Guidance?

Schedule a direct 15-minute scoping consultation with Rohit Kumar to review your enterprise architecture, migration plan, or governance posture.

Book Consultation with Rohit Kumar
Deep Dive: Elevating Your M365 Governance Framework Strategy

When discussing M365 Governance Framework, it is crucial to recognize that the technological landscape is continually shifting. Organizations that fail to adopt modern best practices often find themselves burdened with technical debt, sluggish performance, and significant security vulnerabilities. Implementing M365 Governance Framework successfully is not merely about deploying a tool; it is about enacting a digital transformation that resonates throughout every level of your organization, from frontline workers to the executive suite. Through years of dedicated architectural consulting, I have consistently observed that the most resilient businesses are those that proactively align their M365 Governance Framework initiatives with long-term strategic business goals rather than treating them as isolated IT projects.

Integrating M365 Governance Framework into the Enterprise Ecosystem

In an interconnected digital workplace, M365 Governance Framework does not operate in a vacuum. It must seamlessly integrate with your existing Active Directory (or Entra ID) frameworks, your unified communication platforms like Microsoft Teams, and your broader data governance policies. A fragmented approach often leads to data silos—where information is duplicated, lost, or inappropriately accessed. By establishing a unified architecture, we ensure that M365 Governance Framework acts as a cohesive thread, weaving together various productivity applications into a single, intuitive user experience. This holistic integration significantly reduces the friction typically associated with adopting new technologies.

Future-Proofing Your Architecture

One of the core tenets of my architectural philosophy regarding M365 Governance Framework is future-proofing. Microsoft frequently rolls out updates, new features, and deprecated functionalities. If your environment is heavily customized with rigid, non-standard code, every update becomes a potential point of failure. Therefore, I strictly adhere to out-of-the-box capabilities wherever possible, extending functionality only through officially supported extensibility frameworks like the SharePoint Framework (SPFx) or Microsoft Graph API. This guarantees that your M365 Governance Framework investment will gracefully evolve alongside Microsoft's roadmap, minimizing future maintenance costs and preventing unexpected downtime.

The Human Element: Change Management and Training

No matter how technically flawless a M365 Governance Framework deployment may be, its ultimate success hinges on user adoption. A common pitfall is treating deployment as the final step. In reality, go-live is just the beginning. Comprehensive change management—including targeted training sessions, the identification of power users (champions), and continuous feedback loops—is essential. I work closely with your internal teams to develop customized readiness plans. By demystifying M365 Governance Framework for the end-user and clearly demonstrating its value in their day-to-day tasks, we can accelerate adoption curves and ensure that your organization fully realizes the anticipated return on investment.

Ultimately, my goal as your independent architect is to leave you with a robust, scalable, and highly secure environment. Whether you are in the initial planning stages or looking to remediate a struggling M365 Governance Framework implementation, bringing in specialized, senior-level expertise is the most reliable way to mitigate risk and guarantee success. Let's collaborate to build an intelligent, modern workplace that empowers your workforce and drives tangible business results.

Production Zero-Trust Architecture

Enterprise Governance Work Samples & Security Blueprints

Automated lifecycle provisioning engines, Microsoft Purview DLP enforcement, Entra ID Conditional Access matrices, and regulatory compliance vaults delivered for global enterprises. Anonymized under NDA.

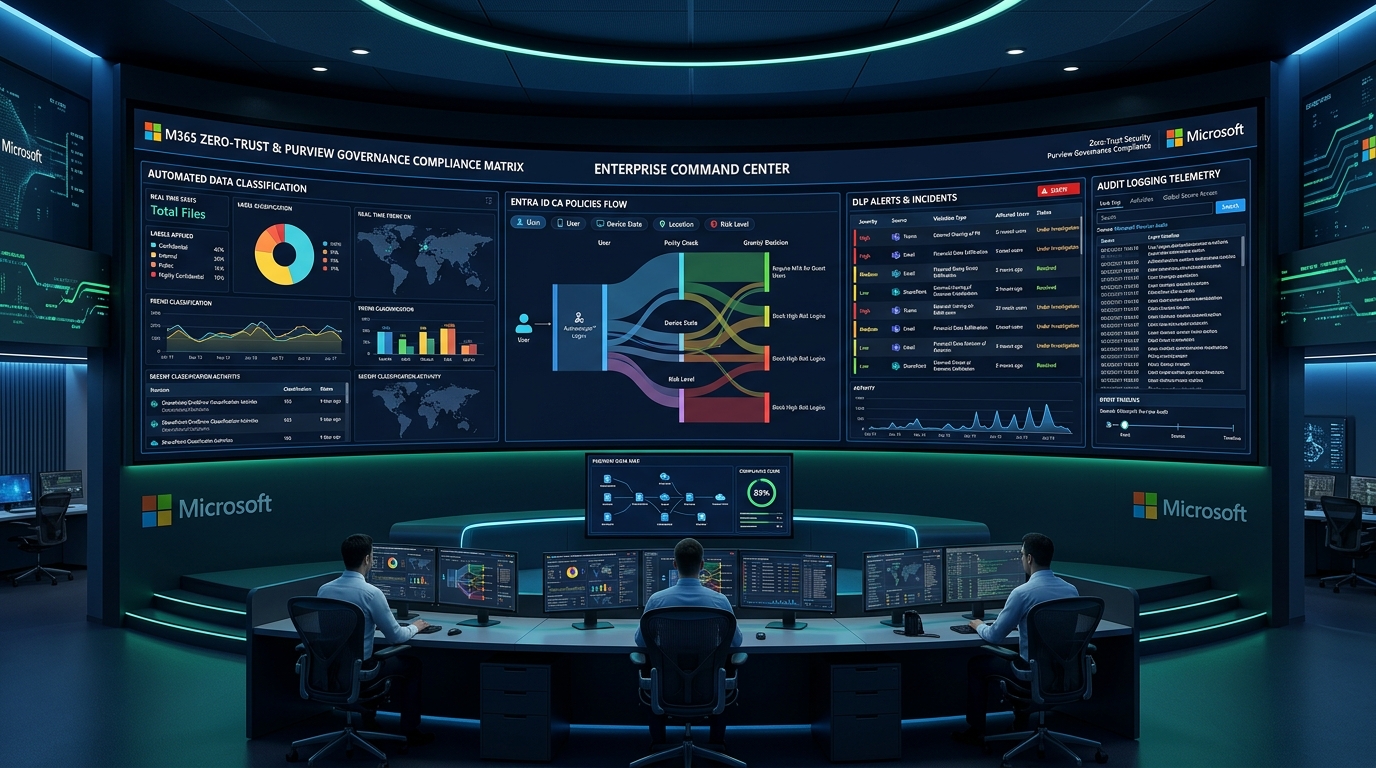
Enterprise Microsoft 365 Zero-Trust Security and Purview Governance Compliance Matrix Dashboard
Security Console Artifact #GOV-SEC-2026
Featured Architectural Solution

Automated Sensitivity Labeling & Purview DLP Compliance Center

Real-time classification telemetry, Entra ID Conditional Access device health verification, automated orphan workspace quarantine, and immutable legal hold enforcement.

Purview • Entra ID • Graph API Request Governance Audit
Financial Holding • 60,000 Users Sample #1

Automated Workspace Lifecycle & Provisioning Engine

Replaced uncontrolled self-service site creation with an automated multi-tier provisioning engine using Power Apps, Graph API, and Logic Apps. Enforces mandatory business justification, secondary ownership, and 180-day inactivity attestation.

Key Deliverable: Custom Teams & SharePoint provisioning wizard with automated URL checks
Sprawl Reduction: Identified and automatically archived 1,400 abandoned sites (24TB freed)
Compliance: 100% of newly created workspaces assigned verified Purview sensitivity labels
Graph API • Power Apps • Logic Apps 1,400 Sites Archived
Healthcare System • 14 Hospitals Sample #2

Zero-Trust Entra ID Conditional Access Matrix

Designed and deployed a comprehensive Conditional Access policy framework locking down SharePoint Online and OneDrive access to Intune-compliant managed endpoints, enforcing step-up FIDO2 MFA for off-network medical personnel.

Key Deliverable: Granular Session Controls restricting unmanaged browsers to view-only (no download)
Risk Protection: Identity Protection policies auto-blocking anomalous geo-velocity sign-ins
HIPAA Defense: Prevented patient health information leakage to unmanaged personal home PCs
Conditional Access • Intune • MFA Zero Data Egress
Retail & E-Commerce • 8M Files Sample #3

Microsoft Purview Automated Sensitivity & DLP

Implemented automated Purview Information Protection classifiers scanning 8M files across SharePoint Online. Automatically applied hardware encryption to files containing credit card numbers (PCI-DSS), SSNs, and executive compensation records.

Key Deliverable: DLP policy blocking external sharing of files with sensitive data patterns
Automated Labeling: 1.2M historical documents classified without manual user effort
User Friction: Configured contextual policy tips guiding users on safe collaboration alternatives
Purview DLP • Auto-Labeling 1.2M Auto-Labeled
High-Tech Engineering • 1,200 Vendors Sample #4

External Guest Governance & Access Reviews

Resolved a critical audit finding regarding 6,500 unmanaged external B2B guest accounts with persistent access to engineering drawings. Rolled out Microsoft Entra Access Reviews and automated sponsor recertification workflows.

Key Deliverable: Quarterly automated access review campaigns requiring project lead recertification
Exposure Reduction: Automatically revoked 4,800 dormant external vendor accounts
B2B Collaboration: Cross-tenant access settings configured with trusted suppliers only
Entra ID Governance • B2B 74% Exposure Cut
Regulated Banking • SEC 17a-4 Sample #5

Immutable WORM Compliance Vault & eDiscovery

Configured regulatory preservation locks across 350 SharePoint Online site collections to fulfill SEC Rule 17a-4(f) and FINRA 4511 write-once-read-many (WORM) storage mandates. Included legal hold custodians and Purview eDiscovery workflows.

Key Deliverable: Regulatory Preservation Lock preventing deletion even by Global Administrators
eDiscovery Premium: Advanced custodian mapping and optical character recognition (OCR) indexing
Audit Defense: SEC formal examination passed with formal compliance officer attestation
WORM Storage • Purview eDiscovery SEC Compliant

Audit-Defensible Governance in 30 Days

Stop guessing your security posture. Enforce automated lifecycle, Purview labeling, and Zero-Trust access controls that pass audits without crippling productivity.

Governance & Purview Advisory

Frequently Asked Questions: Microsoft 365 Enterprise Governance

Actionable architecture answers on Purview sensitivity labels, DLP boundaries, guest access, and tenant sprawl prevention.

What are the core pillars of an enterprise Microsoft 365 governance framework?

The four core pillars are: (1) Identity & Access Management via Entra ID PIM and Conditional Access, (2) Information Protection through Purview sensitivity labels and DLP, (3) Workload Lifecycle Governance for SharePoint sites and Microsoft Teams, and (4) Auditing and Continuous Compliance reporting.

How do Purview Sensitivity Labels prevent unauthorized data oversharing in SharePoint Online?

Sensitivity labels apply persistent cryptographic encryption and rights management to documents. Even if an encrypted document is downloaded to an unmanaged personal device or attached to an email, only authenticated corporate users with verified credentials can decrypt and view the payload.

How does automated Teams & SharePoint site lifecycle governance prevent sprawl?

Automated lifecycle governance uses Entra ID group expiration policies, quarterly access reviews for external guests, and Power Automate approval workflows for new site provisioning, automatically archiving or deleting orphaned and inactive workspaces after 180 days.

What is the recommended approach to external guest sharing without exposing tenant data?

Enforce Entra B2B collaboration with domain allow-listing, mandatory MFA for all guest identities, SharePoint tenant-wide restriction to 'Specific People' links only, and automated Purview access reviews that revoke guest permissions if inactive for 90 days.

How does M365 governance directly support Microsoft Copilot readiness?

Microsoft Copilot honors all underlying user permissions. Without strict governance and sensitivity labeling, Copilot can inadvertently summarize confidential executive compensation or strategic documents for standard employees who were granted over-permissive 'Everyone except external users' read access.

Ready to Get Started?

Let's discuss how we can help with your Microsoft 365 needs

Contact Me
Direct Principal Engagement 18+ Yrs Experience · Zero Junior Handoffs

Enterprise Architecture Discovery & 1-on-1 Mentorship

Connect directly with Rohit Kumar for enterprise SharePoint & Power Platform scoping, zero-downtime migration runbooks, or personalized PL-600 & SC-300 exam coaching.